This post will guide you through the skill assesment of the JavaScript Deobfuscation module of HTB Academy. For this assesment I will do use of curl.
- 1. Try to study the HTML code of the webpage, and identify used JavaScript code within it. What is the name of the JavaScript file being used?
- 2. Once you find the JavaScript code, try to run it to see if it does any interesting functions. Did you get something in return?
- 3. As you may have noticed, the JavaScript code is obfuscated. Try applying the skills you learned in this module to deobfuscate the code, and retrieve the ‘flag’ variable.
- 4. Try to Analyze the deobfuscated JavaScript code, and understand its main functionality. Once you do, try to replicate what it’s doing to get a secret key. What is the key?
- 5. Once you have the secret key, try to decide it’s encoding method, and decode it. Then send a ‘POST’ request to the same previous page with the decoded key as “key=DECODED_KEY”. What is the flag you got?
1. Try to study the HTML code of the webpage, and identify used JavaScript code within it. What is the name of the JavaScript file being used?
The first thing I did is to make a curl request and grep by script finding the flag.
curl -sSvf 154.57.164.65:40515 G script
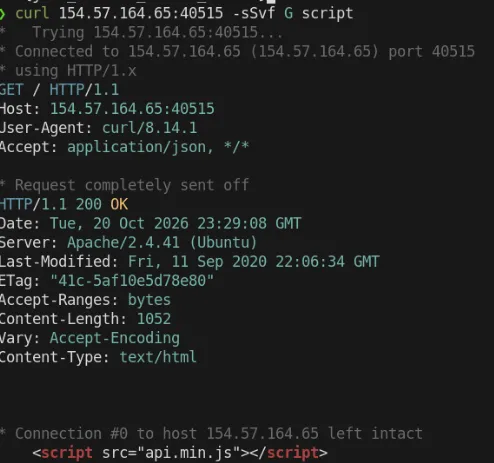
Flag
api.min.js
2. Once you find the JavaScript code, try to run it to see if it does any interesting functions. Did you get something in return?
I copied the javascript content in a javascript console and wrapping it with eval() to execute the function it had.
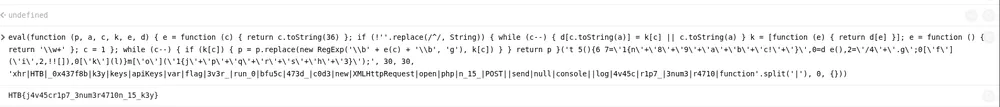
Flag
HTB{j4v45cr1p7_3num3r4710n_15_k3y}
3. As you may have noticed, the JavaScript code is obfuscated. Try applying the skills you learned in this module to deobfuscate the code, and retrieve the ‘flag’ variable.
Using the online webcrack tool I deobfuscated the JS code and executed a console log to obtain the response of the function.
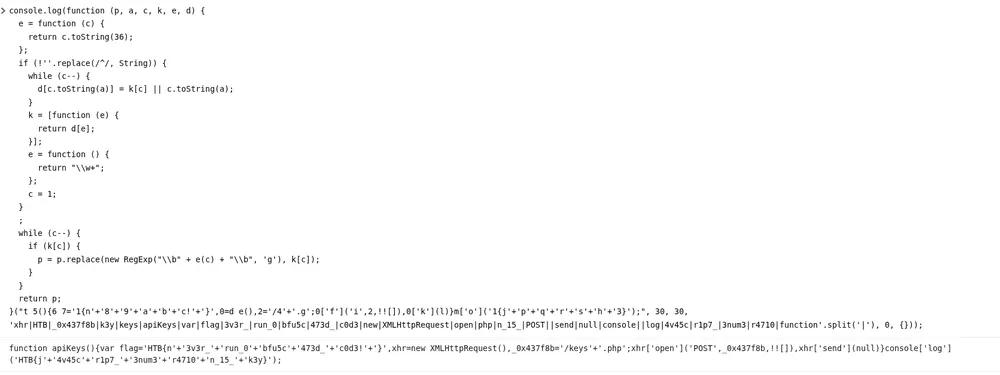
The following command would delete the quotes and get the final flag.
echo "HTB{n'+'3v3r_'+'run_0'+'bfu5c'+'473d_'+'c0d3!'+'}'" | tr -d "'+'"
Flag
HTB{n3v3r_run_0bfu5c473d_c0d3!}
4. Try to Analyze the deobfuscated JavaScript code, and understand its main functionality. Once you do, try to replicate what it’s doing to get a secret key. What is the key?
Here we have to replicate the post request is doing the obfuscated javascript to get the flag.
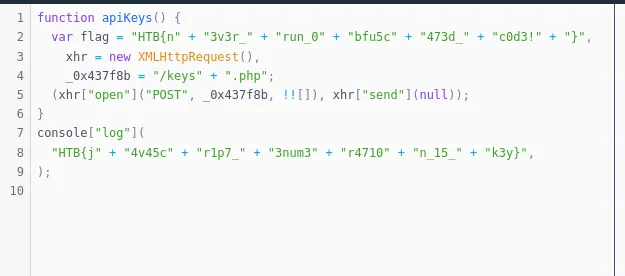
curl 154.57.164.71:43666/keys.php -X POST
Flag
4150495f70336e5f37333537316e365f31355f66756e
5. Once you have the secret key, try to decide it’s encoding method, and decode it. Then send a ‘POST’ request to the same previous page with the decoded key as “key=DECODED_KEY”. What is the flag you got?
I used cyberchef and got the param for the POST request
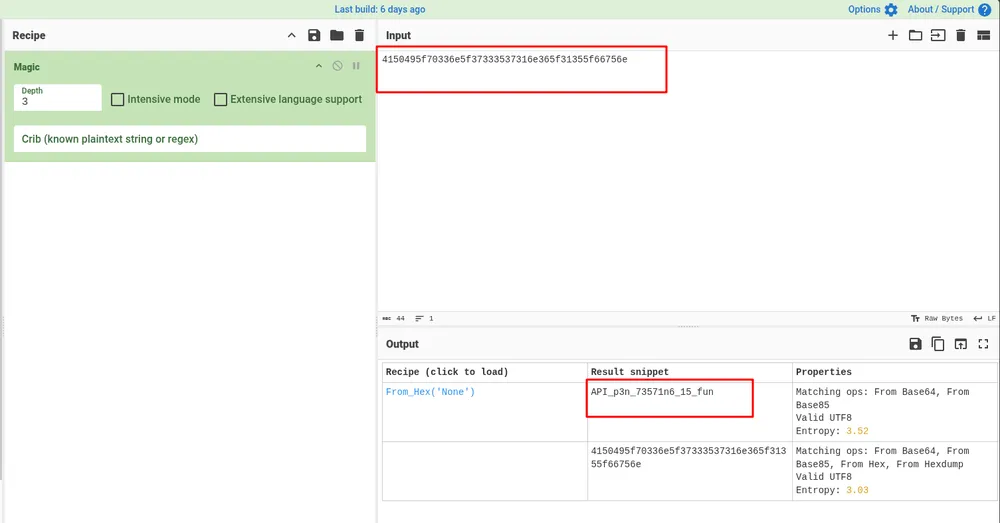
curl 154.57.164.71:43666/keys.php -X POST -d "key=API_p3n_73571n6_15_fun"
Flag
HTB(r34dy_70_h4ck_my_w4y_in_2_HTB)