This post will guide you through the skill assesment of the Web Fuzzing module of HTB Academy.
For this module I will use ffuf as main tool and posting.
After completing all steps in the assessment, you will be presented with a page that contains a flag in the format of HTB{…}. What is that flag?
We only now two things:
The target IP
The
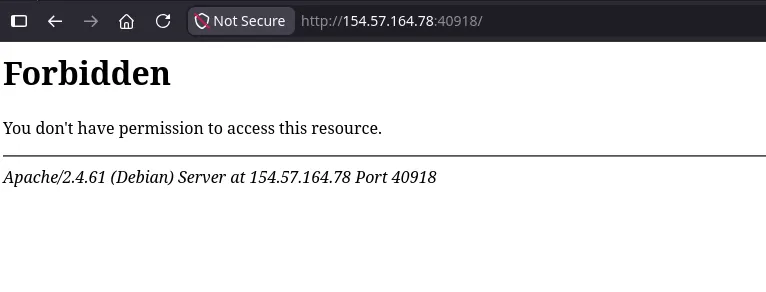
common.txtas main wordlist - The first thing I normally do is to access the IP with the browser. Nothing found
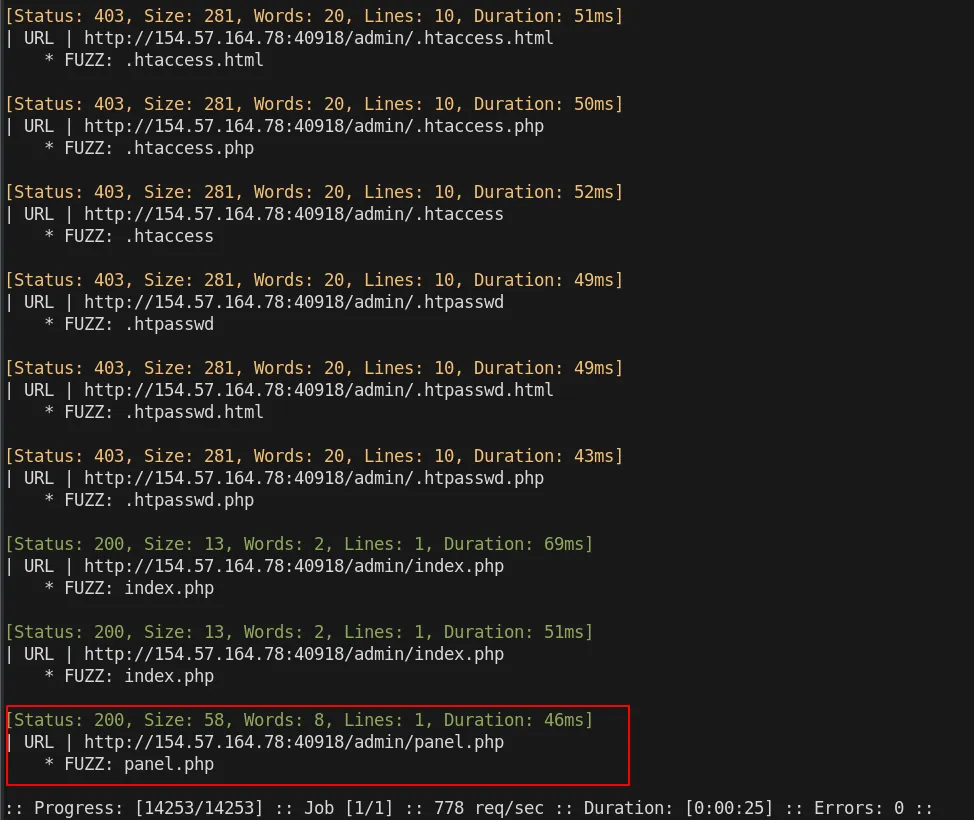
1. I pass to fuzzing directories with recursion. I found /admin/index.php and /admin/panel.php
ffuf -w /usr/share/seclists/Discovery/Web-Content/common.txt:FUZZ -u http://154.57.164.78:40918/admin/FUZZ --ic -c -v --recursion --recursion-depth 3 -e .html,.php
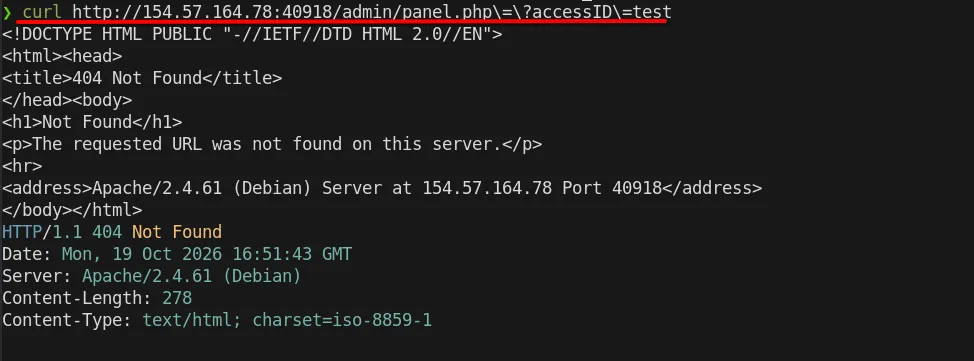
2. It require a paremeter named accessID, but it doens’t specify if it’s by POST or GET. As it’s responding to a GET request I tried directly fuzzing with query string.
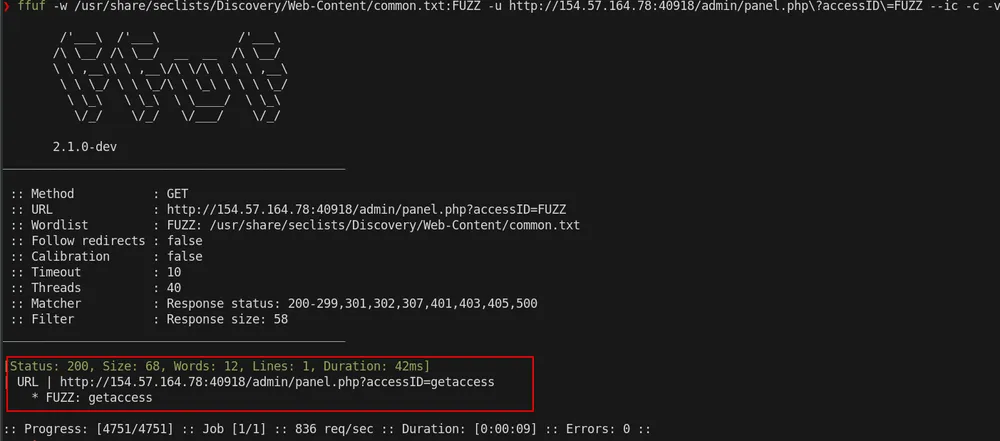
3. I found the value getaccess.
ffuf -w /usr/share/seclists/Discovery/Web-Content/common.txt:FUZZ -u http://154.57.164.78:40918/admin/panel.php\?accessID\=FUZZ --ic -c -v -fs 58
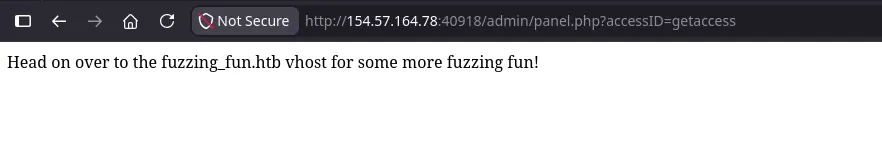
4. Following the clues shown I add the new domain to /etc/hosts and fuzz:
echo "<target_ip> fuzzing_fun.htb" | sudo tee -a /etc/hosts
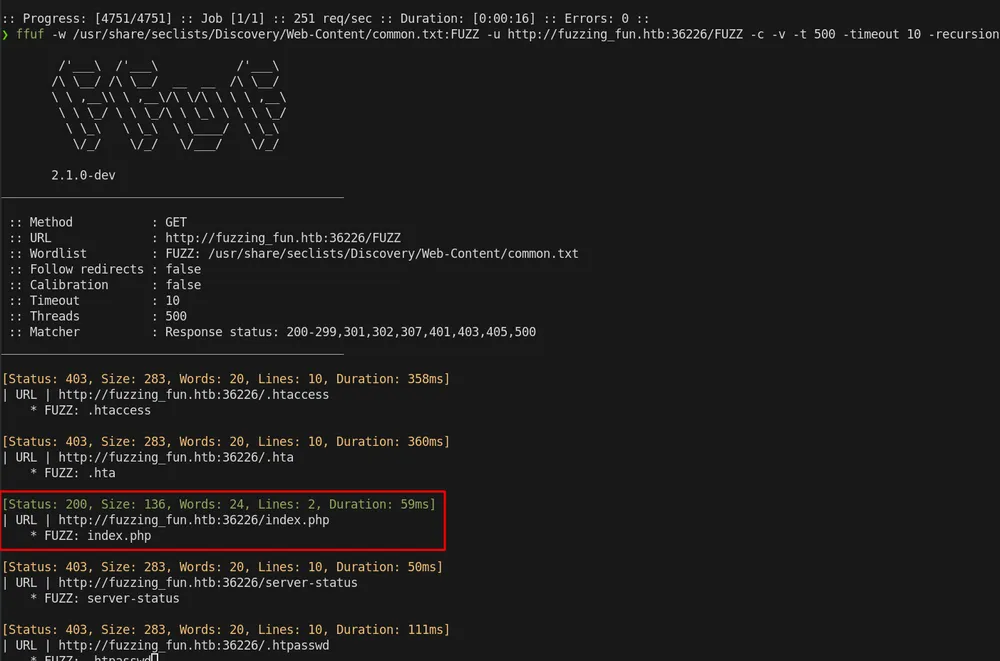
5. I found the folder godeep as next step, but it tell us an important message, we have to search for this directory in other vhost.
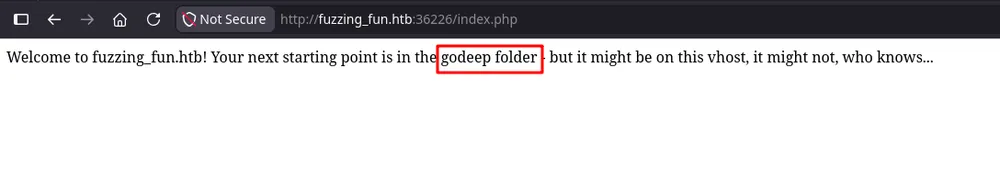
6. I fuzz to search the vhost and I found hidden.fuzzing_fun.htb.
ffuf -w /usr/share/seclists/Discovery/Web-Content/common.txt:FUZZ -u http://154.57.164.74:36226/godeep/ -c -v -t 500 -timeout 10 -H "Host: FUZZ.fuzzing_fun.htb"
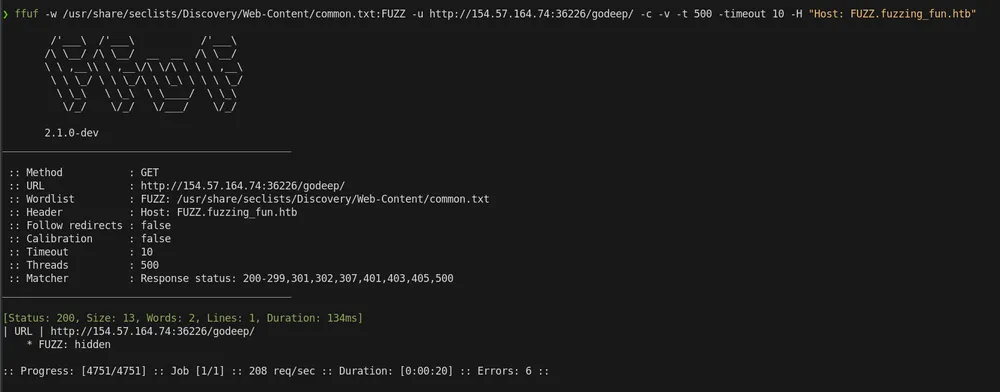
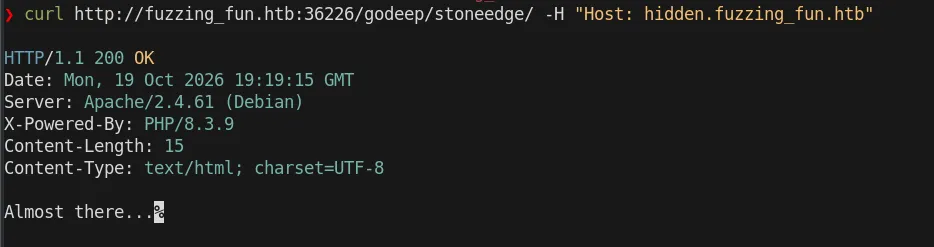
7. Subsequently I fuzz subfolders for the virtual host found previously. FirstIy I uncrossed the subdirectory stoneedge.
ffuf -w /usr/share/seclists/Discovery/Web-Content/common.txt:FUZZ -u http://154.57.164.74:36226/godeep/FUZZ -c -v -t 500 -timeout 10 -H "Host: hidden.fuzzing_fun.htb"
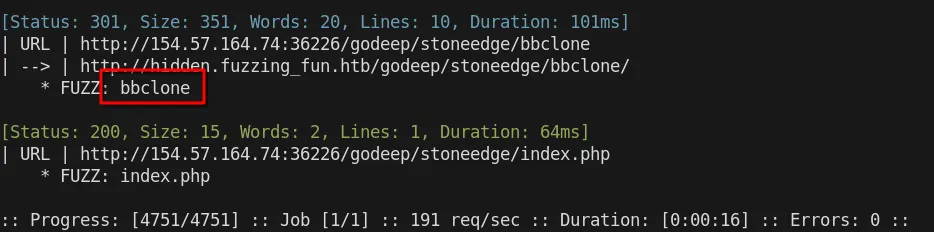
8. Secondly the subdirectory bbclone.
ffuf -w /usr/share/seclists/Discovery/Web-Content/common.txt:FUZZ -u http://154.57.164.74:36226/godeep/stoneedge/FUZZ -c -v -t 500 -timeout 10 -H "Host: hidden.fuzzing_fun.htb"
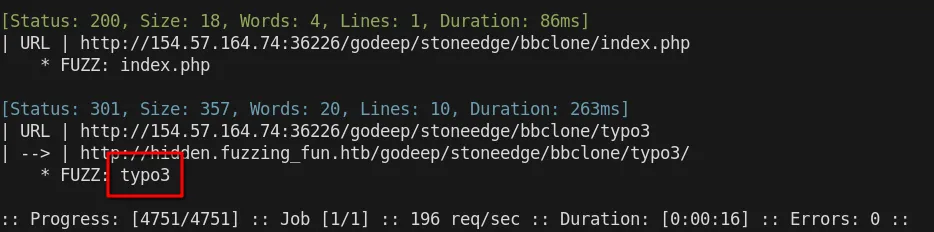
9. And finally the subdirectory typo3.
ffuf -w /usr/share/seclists/Discovery/Web-Content/common.txt:FUZZ -u http://154.57.164.74:36226/godeep/stoneedge/bbclone/FUZZ -c -v -t 500 -timeout 10 -H "Host: hidden.fuzzing_fun.htb"
10. With the full path http://$ip:$port/godeep/stoneedge/bbclone/typo3/ and the suitable virtual host, I got the flag using posting.
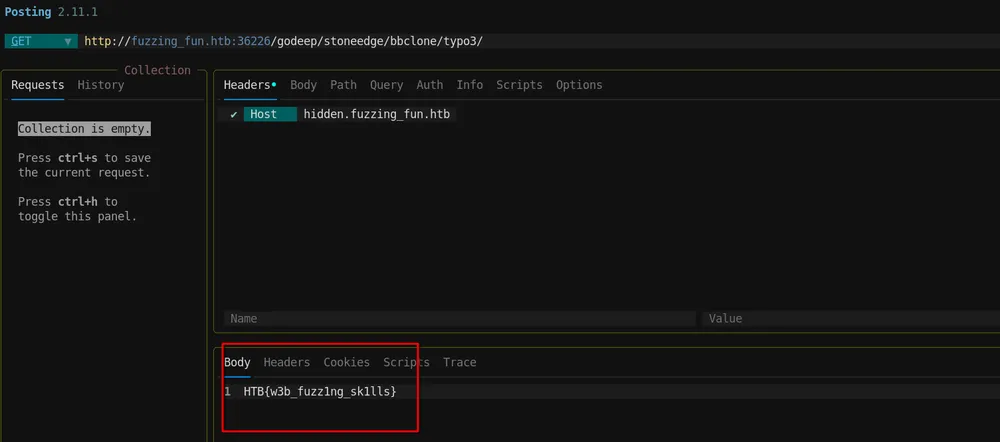
Flag
HTB{w3b_fuzz1ng_sk1lls}